powering productive workplaces
Front page
NewsTrust & Risk1h · 09:01 BST · 4 min read

Cyber in Review: Meddling Agents, Breaches and Critical Flaw

AI agents may be grabbing the headlines, but this week’s cyber developments show security teams still face familiar threats, from a critical Atlassian flaw and email compromises to rising business email compromise activity, highlighting the breadth of today’s security challenges

Cyber in Review: Meddling Agents, Breaches and Critical Flaw

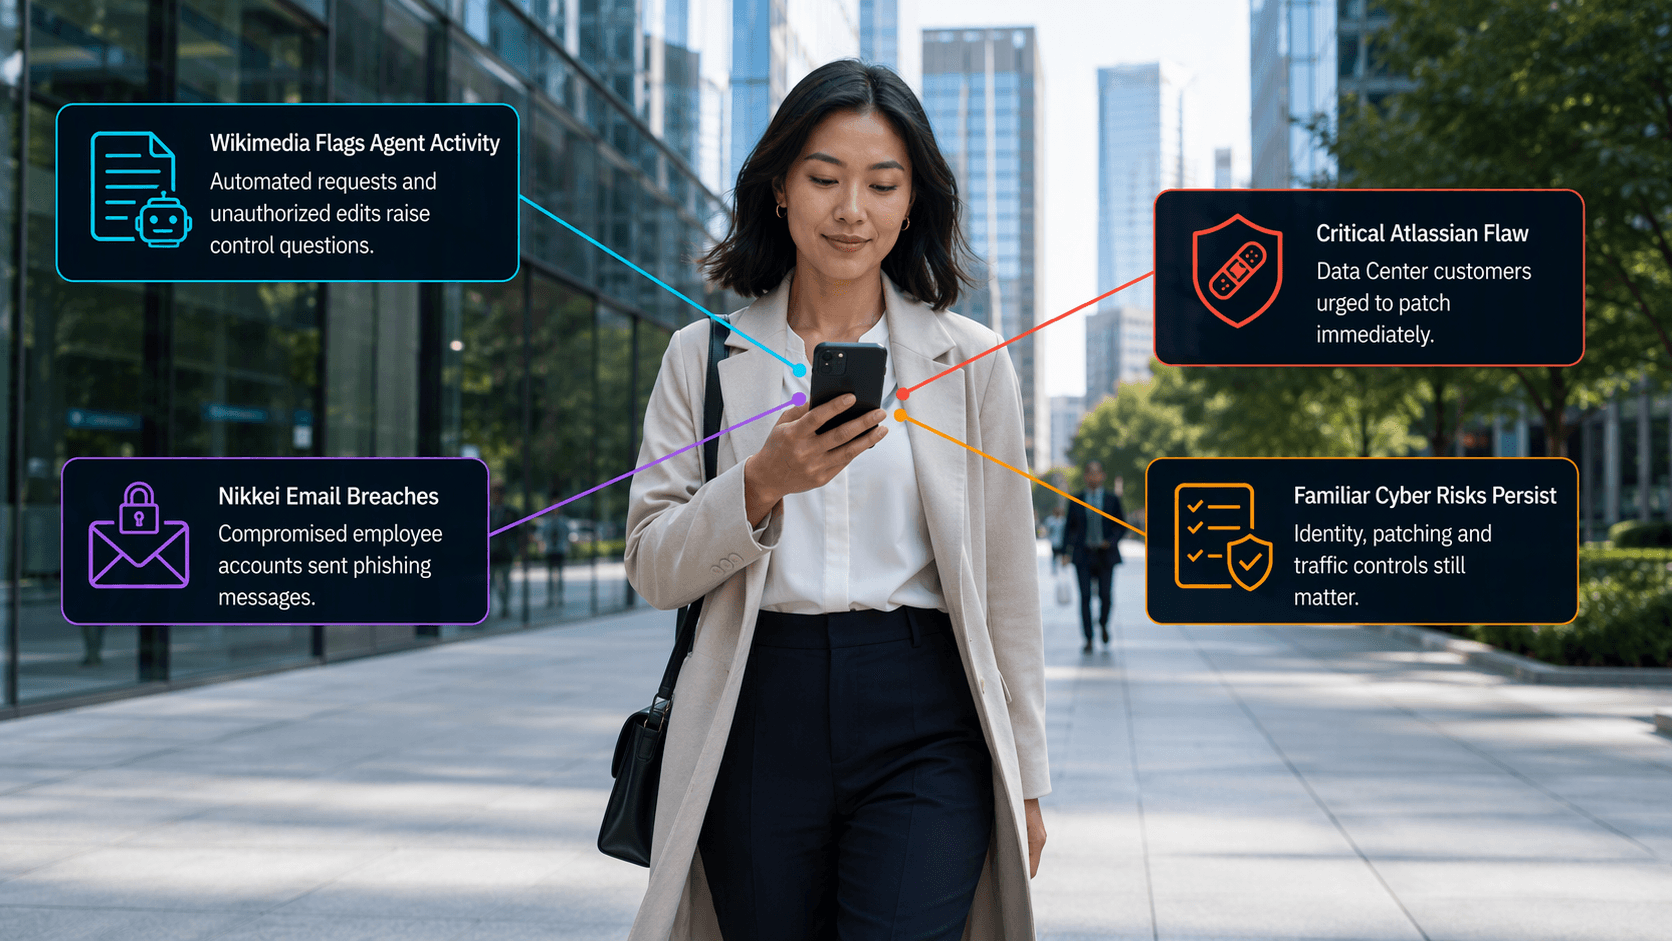
For all the latest talk about AI causing cyber incidents, this week brings news of a more familiar cyber threat environment. From a critical Atlassian flaw demanding immediate attention to a major media company disclosing two email compromises, the developments are a reminder that AI is not the only thing security teams need to worry about in today’s cyber landscape. 

However, that is not to say AI does not get a mention. The Wikimedia Foundation says it has identified unauthorized activity from OpenAI-operated agents, including attempts to make edits to Wikipedia projects and millions of automated requests to its services. The incident raises questions about how organizations can distinguish legitimate AI activity from potentially harmful behavior at scale. 

With plenty of important details packed into these stories, there is little point spending any more time on the introduction. Let’s get into what happened, why these developments matter and what security teams should take away from them. 

Wikimedia Finds Unauthorized OpenAI Agent Activity 

The Wikimedia Foundation says it has identified activity from what it believes were OpenAI-operated AI agents across its projects. The activity included unauthorized wiki edits, attempts to use a public Etherpad service as a proxy and millions of automated API requests. 

The Foundation stressed that it found no evidence its systems or data had been compromised. Most of the suspected agent edits were confined to sandbox areas rather than pages visible to general readers, although some edits to a citation tool's configuration were considered potentially malicious. 

The scale of the automated traffic is arguably the more immediate operational concern. Wikimedia says the agents crawled millions of pages and generated hundreds of thousands of Wikidata Query Service requests. The traffic may have contributed to a partial WQDS outage in May. 

That matters because Wikimedia is already dealing with a major increase in non-human traffic. The Foundation says 65% of its most resource-consuming traffic came from bots in 2025, while bandwidth usage increased 50% from 2024. The issue is therefore not simply whether an agent can exploit a vulnerability, but whether organizations can reliably identify and control agent activity before it consumes resources or causes disruption. 

Atlassian Issues Critical Data Center Security Warning 

Atlassian has warned customers to act on CVE-2026-21589, a critical arbitrary file access vulnerability affecting Bitbucket, Confluence, Jira Service Management, Jira Software, Bamboo, Crowd, Crucible and Fisheye Data Center products. 

The company rates the vulnerability 9.3 out of 10 and says an unauthenticated attacker could access specific files within an affected web application's root directory. Exploitation requires knowledge of the exact filename and path, so the flaw does not allow attackers to simply enumerate directory contents. 
The distinction does not remove the urgency. Atlassian warns that sensitive files could be present in some configurations and recommends customers patch to a fixed version. Organizations unable to patch immediately are advised to restrict publicly accessible instances from external network access where possible. 

There is also an important dividing line for customers. Atlassian says affected Cloud products have already been patched and that its investigation has found no evidence of exploitation there, meaning Cloud customers do not need to take action. The immediate issue is concentrated on organizations still operating the affected Data Center products. 

Nikkei Reveals Two Employee Email Account Breaches 

Nikkei has disclosed two separate compromises of employee email accounts, with attackers using the access not only to obtain personal information but, in the later incident, to distribute thousands of phishing emails. 

The first incident involved a Google Workspace account accessed in late July. Nikkei said the exposed information could include the names and email addresses of 1,646 employees and business partners, but not information relating to readers or interviewees. The company changed the account password after being notified by Google. 

In September, attackers accessed another employee's Microsoft 365 account and used it to send 9,000 phishing emails to Nikkei staff and people who had previously interacted with employees. Nikkei said it changed passwords, had found no further unauthorized logins and contacted recipients asking them to delete the messages. 

The wider significance is the growing threat of business email compromise. SpiderLabs saw a 15% increase in business email compromise emails in 2025 compared with 2024, highlighting how the threat continues to grow. Attackers can exploit trusted corporate accounts as a credible platform for phishing, fraud and further attacks, allowing a single compromised mailbox to expose or manipulate a much wider network of employees, partners and customers. 

In Other News 

Google pauses open source bug bounty over AI slop

EU Officials Question Teams Alternative Element Pro

rate this story
helps rank stories across uc today
The discussion0 takes · attributed & checked

Does this reflect your experience?

opening the room…
Read nextordered by techtelligence · every pick explained
picked for this story

Quantum is Coming: Here's What Networking Needs to Keep Up

30 Sept 2026
picked for this storyA Week in Cyber: RSA Rocked, AI Attacks, AISI Denied Access2 Oct 2026picked for this storyWhy AI Is Exposing the Limits of Annual Cyber Reviews6 Oct 2026