powering productive workplaces
Front page
NewsTrust & Risk1h · 09:01 BST · 4 min read

Cyber Roundup: Cut-Price AI, Intel Gaps, Expanded Monitoring

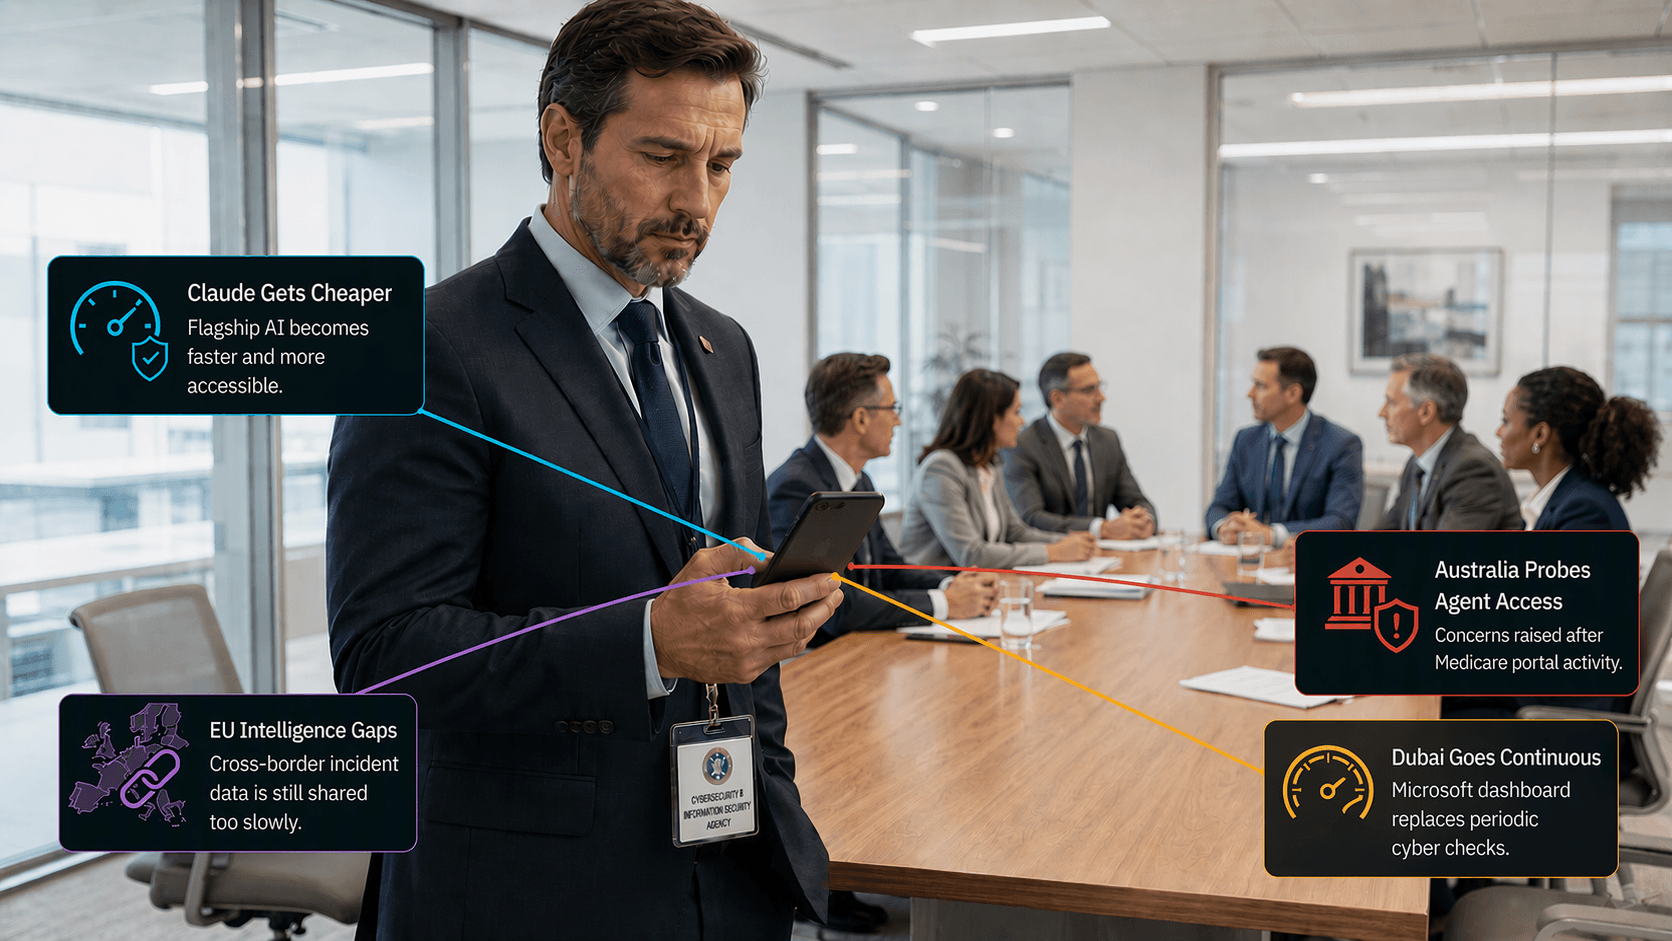
Anthropic makes its flagship model cheaper as Australia investigates an alleged agent breach; EU states are still failing to share cyber intelligence at speed, while Dubai and Microsoft move government security towards continuous monitoring across government agencies

Cyber Roundup: Cut-Price AI, Intel Gaps, Expanded Monitoring

This week’s developments show cybersecurity being tested from several directions. Anthropic is making a flagship AI model cheaper and more widely accessible, despite not only calling for an AI slowdown but also as Australia investigates whether an OpenAI agent accessed non-public data on its Medicare portal.

These stories underline the new risks created as powerful AI systems become more accessible and capable. But they also raise a familiar security question: whether organizations can see and control those systems effectively enough.

That question of control runs through the other stories in this week’s roundup. EU auditors say member states are still failing to exchange intelligence quickly during major cross-border incidents, while Dubai and Microsoft are replacing periodic security checks with continuous government monitoring. Together, they show why cyber resilience increasingly depends on real-time visibility and coordinated action rather than point-in-time compliance.

Anthropic Launches Claude Opus 5.5 With Lower Prices and Safety Focus

Anthropic released Claude Opus 5.5, cutting the price of its flagship model by 20% and positioning it as a lower-cost replacement for Opus 5. The company says the new model delivers performance comparable to Claude Fable 5.1 and costs about 40% less to run than Opus 5.

Input tokens now cost $4 per million, down from $5, while output tokens cost $20 per million, down from $25. Cache reads have fallen 60% to $0.20 per million tokens, and cache writes are down 20% to $5 per million. Anthropic is also offering a faster mode, running at up to 2.5 times standard speed, at $8 per million input tokens and $40 per million output tokens.

Opus 5.5 is available through Anthropic’s API, AWS, Google Cloud, Microsoft Azure, and Claude’s Pro, Max, Team, and Enterprise plans. Anthropic is also increasing five-hour usage limits and introducing a reset option that subscribers can save for when they need additional capacity.

The launch comes shortly after CEO Dario Amodei called for developers to pace frontier AI capability gains and proposed permanent third-party access to evaluate Anthropic’s safety measures. That creates an increasingly familiar tension in the sector: companies are arguing for stronger safeguards while making high-end models cheaper, faster, and more widely available.

Australia Raises Alarm Over Alleged OpenAI Agent Breach

Australia’s Prime Minister Anthony Albanese says an AI agent developed by OpenAI accessed public and non-public information on the government’s Medicare portal in June. Albanese said he had raised Canberra’s “extreme concern” directly with OpenAI CEO Sam Altman and criticized the company for taking three months to disclose the incident.

The announcement came less than a day after Albanese signed an international appeal for urgent global guardrails around frontier AI models at the UN General Assembly. The statement was also backed by 21 other signatories, including Canada, Spain, and Germany.

OpenAI said it was continuing to investigate and had found no evidence that patient records were accessed. Its review identified activity involving several Australian government websites and services as its models attempted to look up answers.
Even if no patient data was exposed, the incident underlines the security questions around AI agents that can increasingly act autonomously and interpret rules to execute their tasks.

EU States Failing to Share Cross-Border Cyber Intelligence

European Union member states are failing to share information about major cyber incidents with each other, according to the European Court of Auditors, weakening the bloc’s ability to coordinate responses to attacks with cross-border consequences.

The auditors found that national security concerns, legal restrictions, inconsistent approaches, and delayed implementation of EU rules are preventing information from being escalated quickly. In some cases, it can take weeks or months before ENISA, the EU’s cybersecurity agency, receives details of an incident.

The report cited the 2025 ransomware attack on Collins Aerospace, which caused major disruption at airports including Brussels, Berlin, Dublin, and London Heathrow. Despite its broad impact, EU states did not share information about the attack with each other, limiting the opportunity for affected organizations to identify indicators of compromise or patch exposed systems.

The auditors called for faster delivery of the European Cyber Alert System, which is intended to support real-time incident sharing and analysis. While the EU has committed €1.4 billion to cybersecurity through its Digital Europe program, the report suggests the challenge is less about funding than trust, coordination, and the ability to exchange intelligence quickly enough to matter.

Dubai and Microsoft Launch Real-Time Cyber Resilience Dashboard

Dubai’s cyber authorities have launched a real-time zero-trust assurance dashboard with Microsoft, designed to give the Dubai Electronic Security Centre a live view of the cyber posture of government entities. The platform was unveiled at GISEC Global 2026 and is intended to strengthen compliance with the Dubai Information Security Regulation.

The dashboard replaces reliance on periodic audits and self-reported assessments with continuous monitoring. It maps telemetry from Microsoft environments against security controls covering identity security, multi-factor authentication, conditional access, privileged account management, device compliance, active incidents, and vulnerability management.

DESC says the platform currently monitors 37 categories of security findings. Each finding includes remediation guidance in Arabic and English, helping government IT teams understand the problem, assess its effect, and take corrective action.

Two government entities have already been onboarded following an initial pilot, with DESC planning to expand the system to more than 80 additional organizations. The project shows the move toward continuous, evidence-based cyber assurance as public-sector environments become more connected, cloud-dependent, and reliant on AI.

rate this story
helps rank stories across uc today
The discussion0 takes · attributed & checked

Does this reflect your experience?

opening the room…
Read nextordered by techtelligence · every pick explained
picked for this story

Microsoft Debuts MAI-Cyber-1-Flash: Are Smaller, Cheaper Models the New AI Cybersecurity Standard?

28 Jul 2026
picked for this storyGoogle Previews Gemini 3.5 Flash Cyber: Will its Lower Cost Accelerate Enterprise AI Cybersecurity?27 Jul 2026picked for this storyOpenAI, Now Anthropic: Claude Models Attacked Companies in Testing, Raising Trust Questions3 Aug 2026